palaniappan p6 min
How to Configure AWS WAF for API Protection (Beyond the Basics)
WAF beyond “enable managed rules”: COUNT→BLOCK, rate limits, Bot Control cost traps, GraphQL depth. July 2026 API protection checklist.
Tagged
WAF beyond “enable managed rules”: COUNT→BLOCK, rate limits, Bot Control cost traps, GraphQL depth. July 2026 API protection checklist.
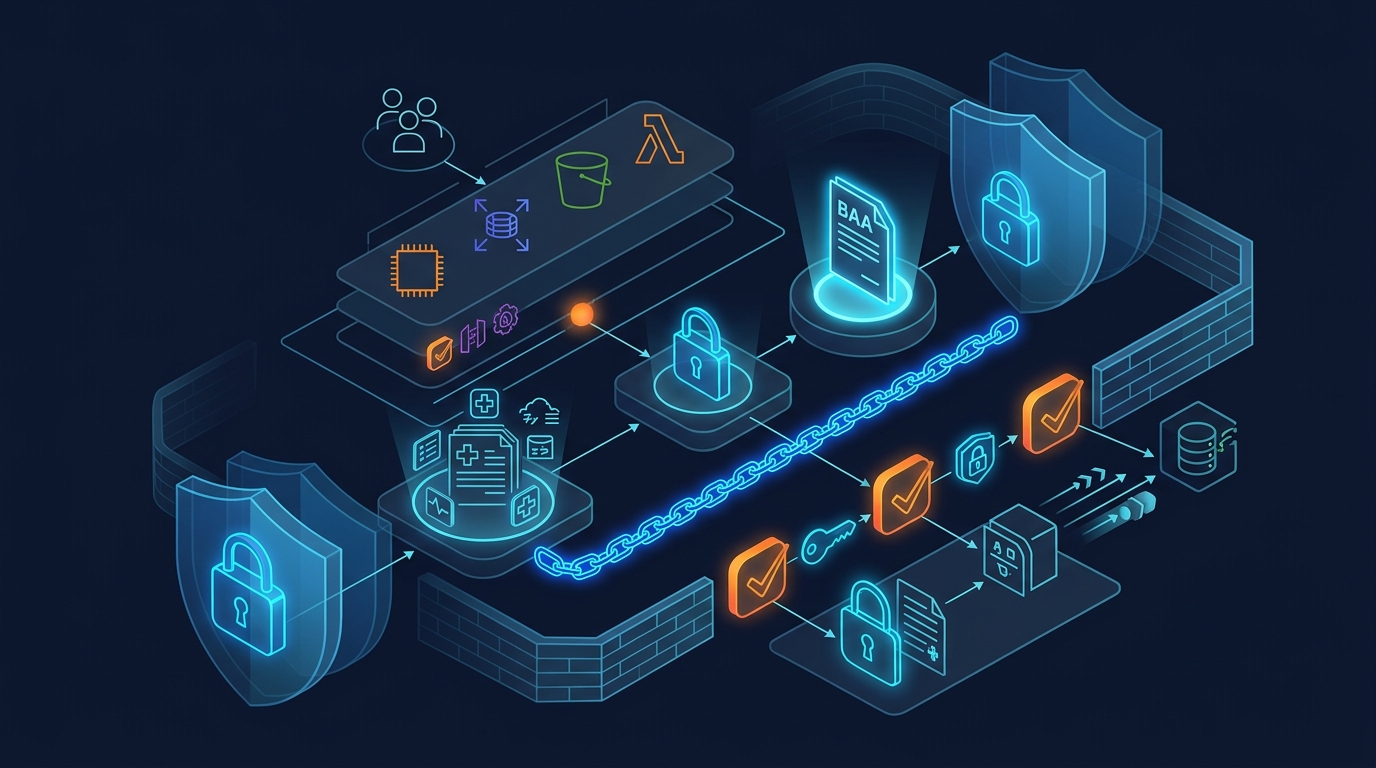
HIPAA on AWS build guide: BAA via Artifact, eligible services, KMS/VPC/RDS/S3 patterns. July 2026 engineering checklist.
Amazon Bedrock Guardrails protect foundation models from harmful outputs — filtering on prompt injection, jailbreaks, toxicity, and PII. This guide covers setup, testing, cost optimization, and production safety patterns for GenAI applications.
AWS Control Tower automates multi-account management — setting up guardrails, enforcing compliance policies, and centralizing billing. This guide covers setup, customization, and production governance patterns.
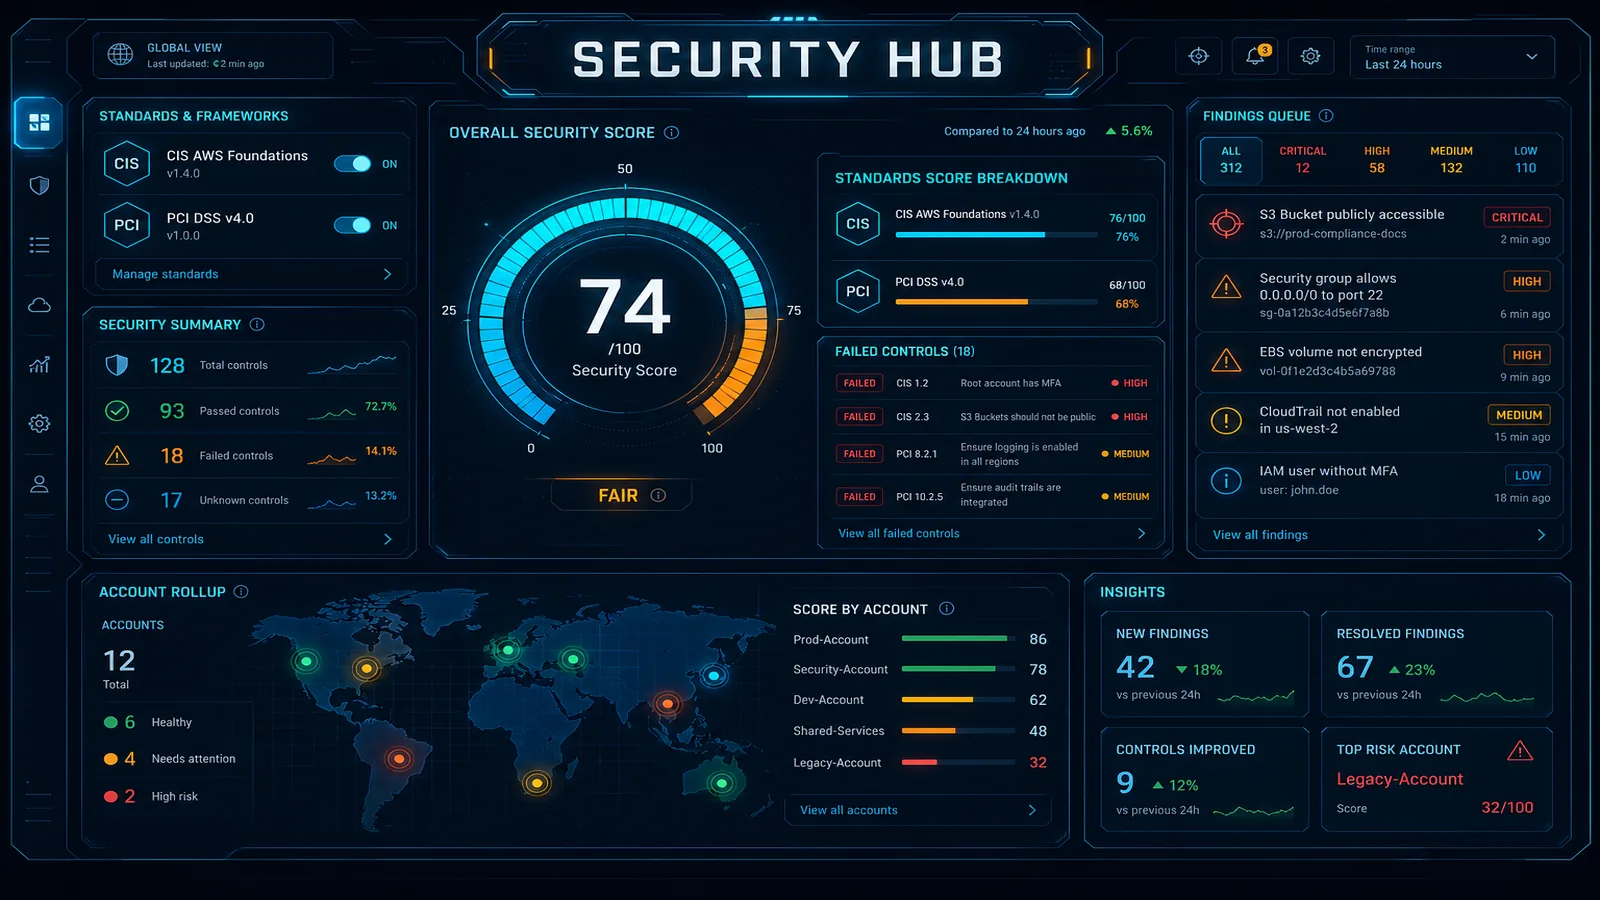
AWS Security Hub aggregates security findings from 200+ sources and, as of Jul 14 2026, includes AI inventory for org-wide AI assets. This guide covers setup, compliance standards, AI inventory, automated remediation, and a compliance dashboard without hiring a SOC team.
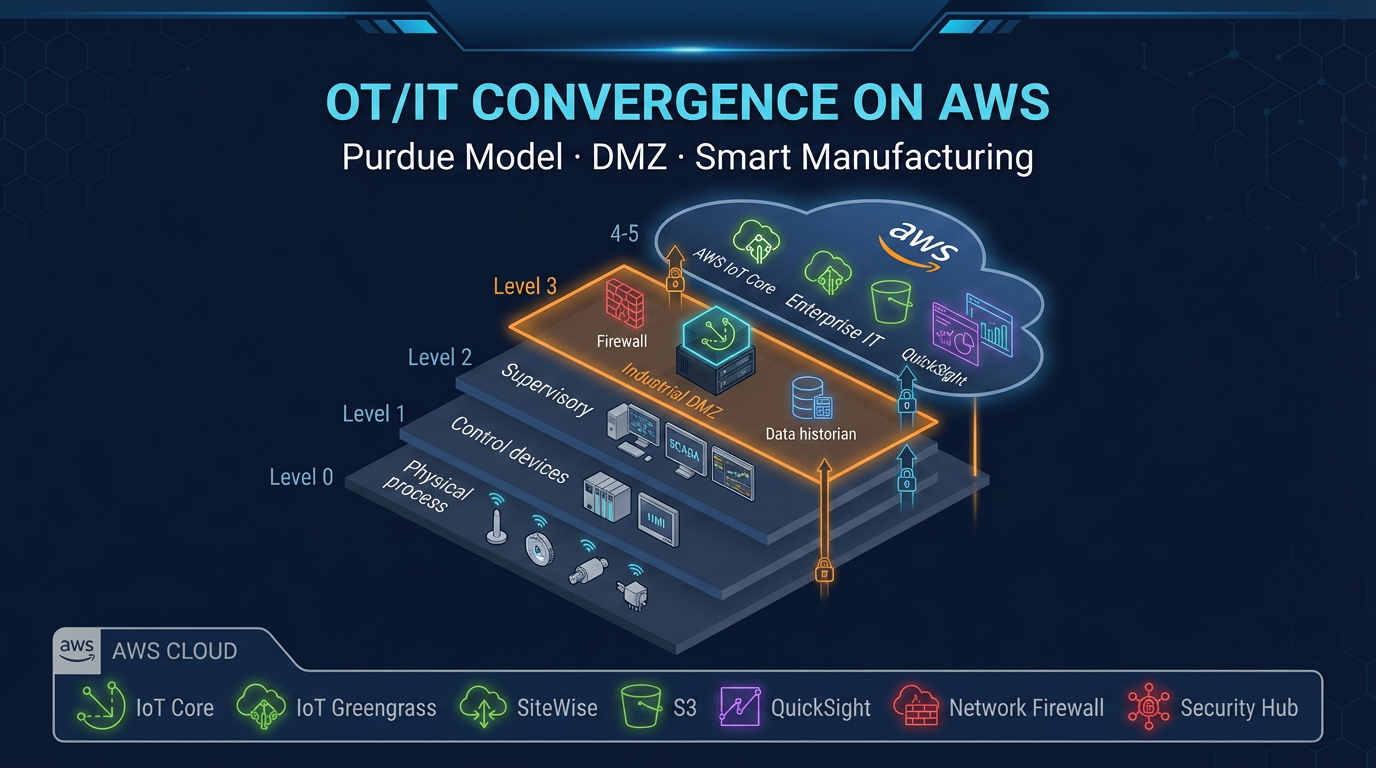
Connecting your operational technology (OT) network to cloud-scale IT systems on AWS is the foundation of smart manufacturing — but it introduces serious security risks if done wrong. Here are the proven architecture patterns.
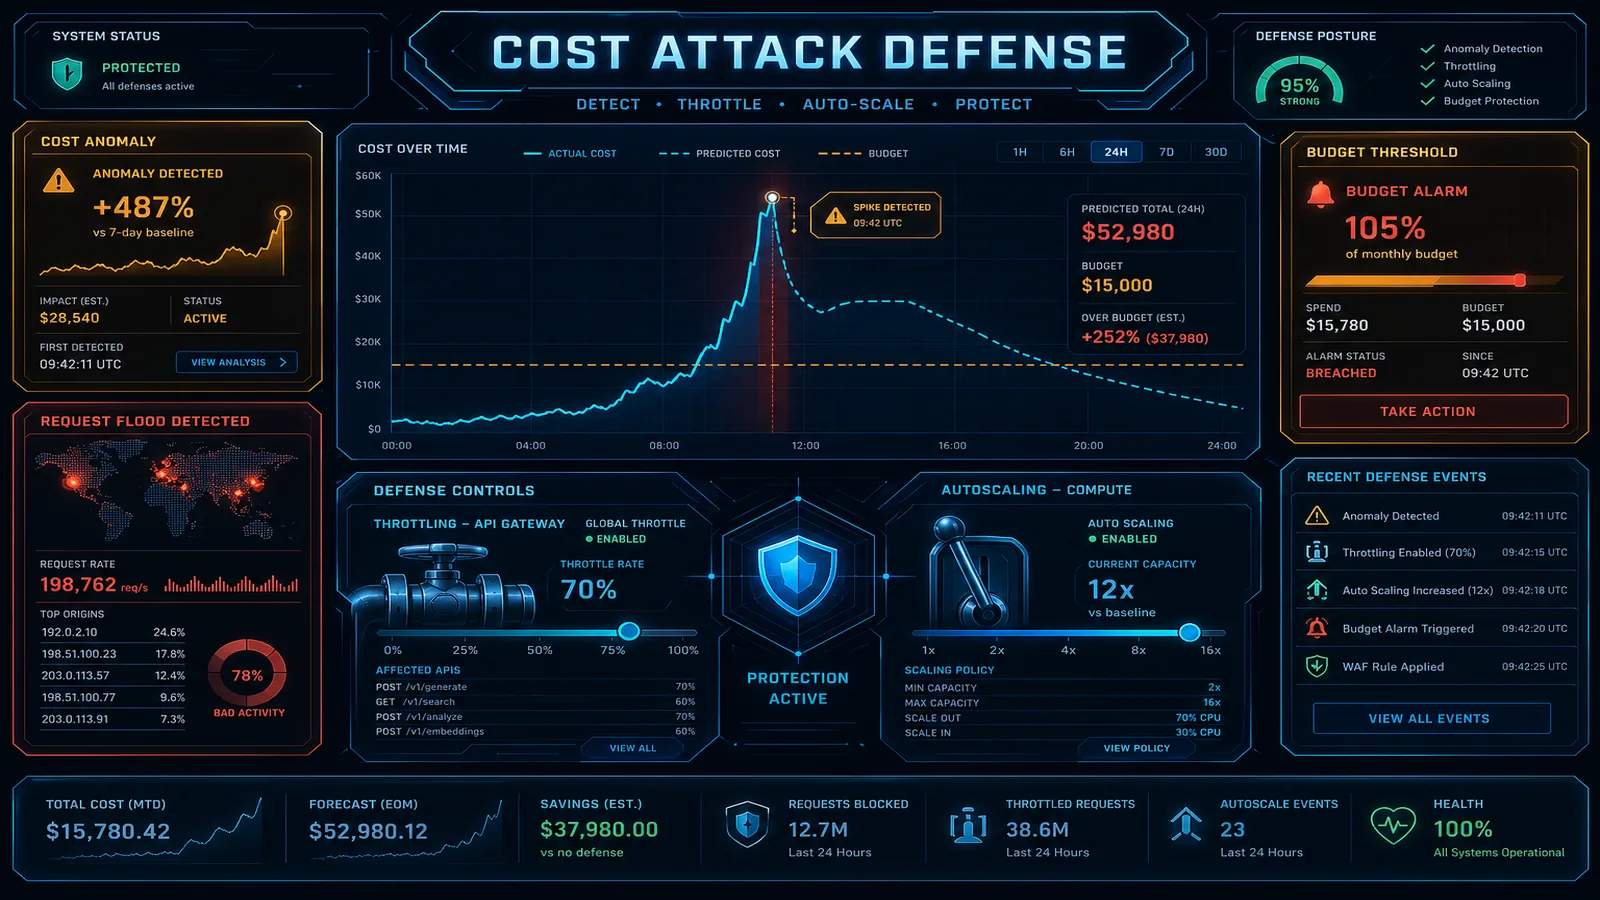
Billing attacks: CloudFront request floods, Lambda bombs, SQS/SNS OTP spam. July 2026 — WAF ceilings, reserved concurrency, Budgets Actions, FinOps backstops.
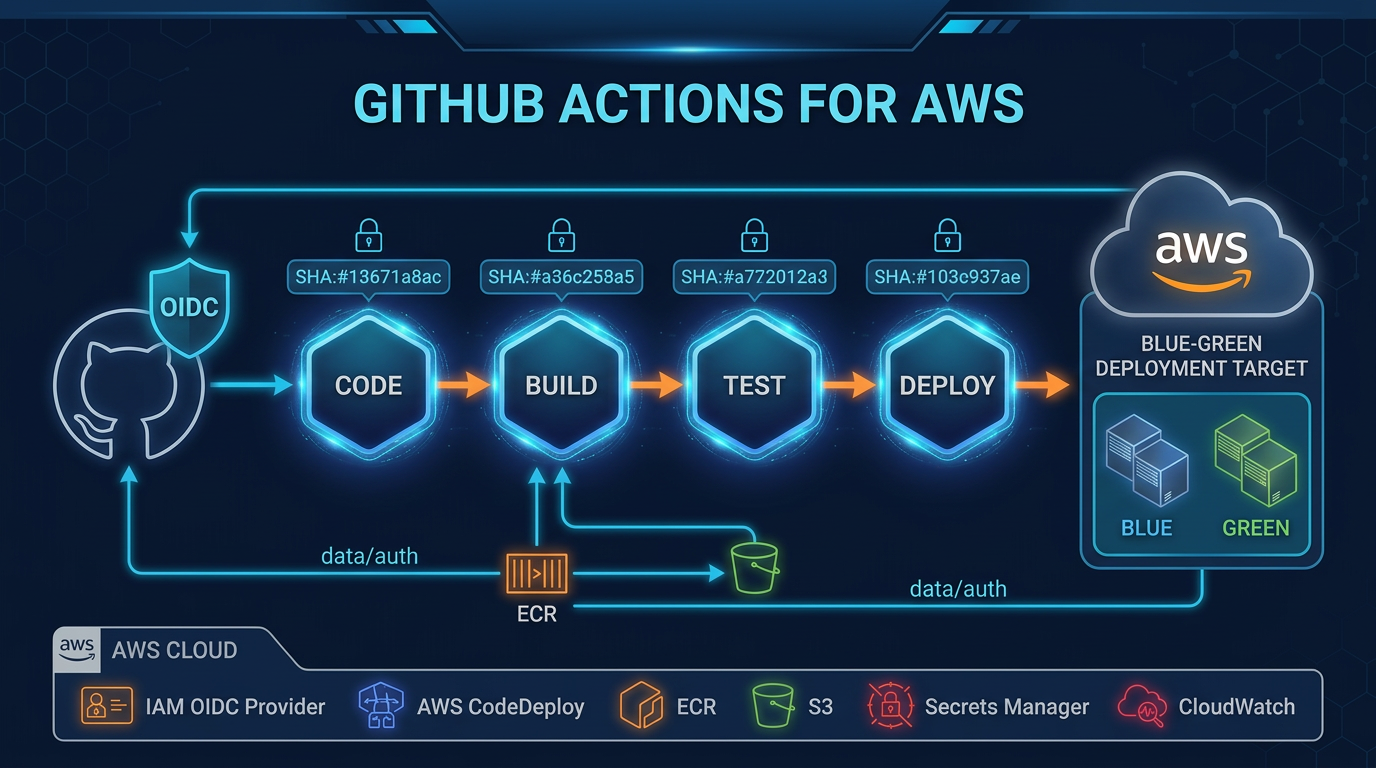
Production-grade GitHub Actions patterns for AWS workloads — OIDC authentication, pinned actions, blue-green deployments, build caching, and the security mistakes that leave your pipeline open to supply chain attacks.
Manual security triage cannot keep up with cloud-scale threats. Here is how to wire GuardDuty Extended Threat Detection, Security Hub, EventBridge, and Lambda into a self-healing AWS security architecture.
Deploying GenAI without guardrails is a compliance incident waiting to happen. Here is how to build a production-grade AI governance layer on AWS using Amazon Bedrock Guardrails, least-privilege IAM, and continuous evaluation.
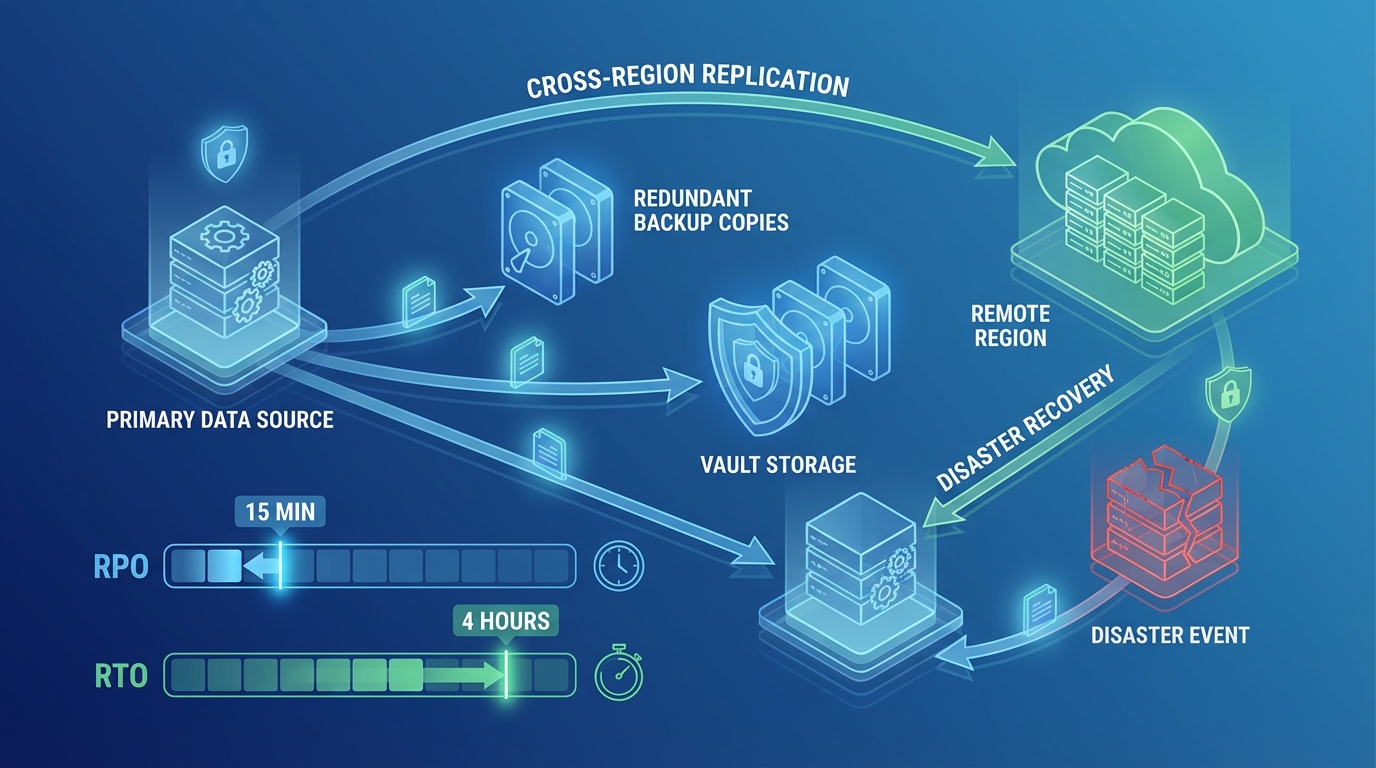
July 2026: AWS Backup plans, Vault Lock, logically air-gapped vaults, cross-account copies, and restore-test cadence — the RPO/RTO discipline that turns “we have backups” into “we restored last week.”
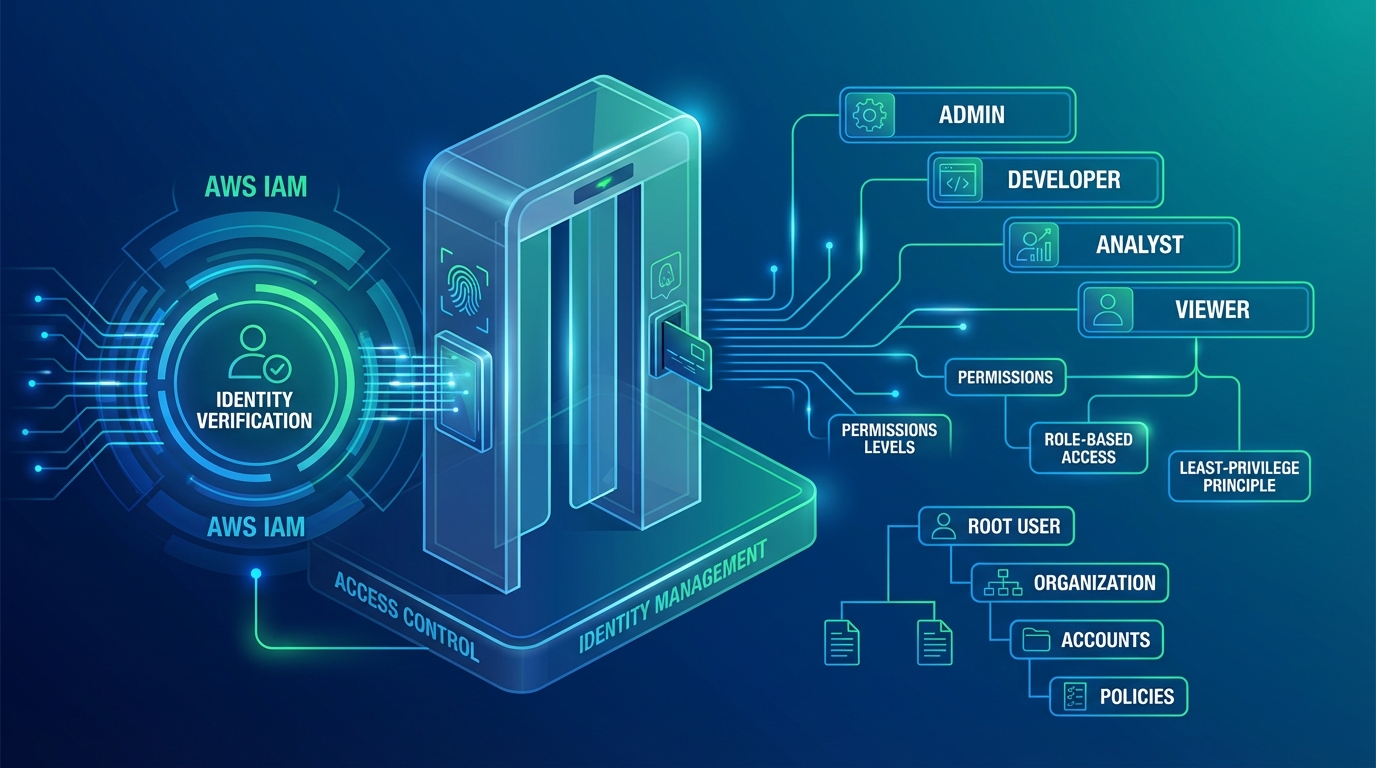
Least privilege is a slogan. Working IAM at production scale is a different problem. Roles vs users, permission boundaries, SCPs, identity federation, and the access-control patterns that keep teams fast without leaving keys lying around.